Vulnerabilities
7 npm Package Mistakes That Expose Your Codebase to Attacks
Most supply chain compromises stem from local dependency management errors rather than external exploits, making your lock files the primary defense line.
Most supply chain compromises stem from local dependency management errors rather than external exploits, making your lock files the primary defense line.
A critical SQL injection flaw in TMS Amelia Booking Plugin versions up to 2.4.10 exposes sites to database manipulation, requiring immediate inventory checks.
AI coding agents introduce vulnerabilities faster than teams can fix them, requiring continuous security checks beyond standard pull request scans.
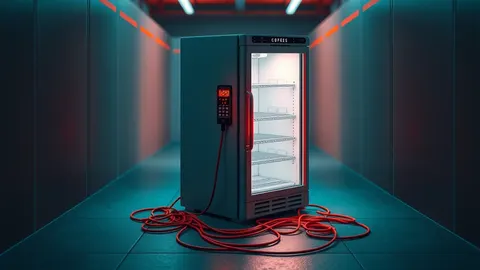
Attackers exploited vulnerabilities in internet-connected fridge units at 700 French stores using flaws flagged by Claroty and CISA in three specific device models.
A critical SQL injection in WeGIA versions prior to 3.8.6 allows attackers to manipulate billing and credential data without authentication.
Microsoft’s October update fixes a record number of flaws, including an actively exploited Windows Shell zero-day that bypasses security warnings.
A critical vulnerability in Frontend Dashboard versions through 3.0.7 allows attackers to escalate privileges, requiring immediate inventory and containment of exposed instances.
Windows applications using .NET 8 through 11 must update NuGet packages to address CVE-2026-70197, a high-severity remote code execution flaw in socket handling.
Two high-severity flaws in Zoom Workplace and My Notes allow unauthenticated attackers to access sensitive data over a network, requiring immediate version checks.
Google releases critical patches for memory corruption bugs in latest desktop builds for Windows, Mac and Linux.
Zero Day Initiative reports three unpatched flaws in Genesis World that enable information disclosure and remote code execution via manipulated file paths.
A stale IOTLB cache in Linux vhost allows local privilege escalation and guest escape, requiring immediate review of virtualized environments using QEMU.
Adobe Experience Manager users must address CVE-2026-106626, a critical input validation flaw allowing privileged attackers to run arbitrary code without interaction.
CVE-2026-102870 allows attackers to run code on developer workstations via the ASP.NET Core debugger; update NuGet packages immediately.
Ivanti confirms zero-day exploitation of CVE-2026-104935, allowing remote command execution without credentials on affected VPN appliances.
Small teams can prioritize patching by focusing only on vulnerabilities that attackers are actively using in the wild right now.
Cross-site scripting fails when the browser treats user input as data rather than executable code, breaking the attack chain before any payload runs.
Authentication bypass flaws often stem from predictable logic errors in code rather than complex cryptographic weaknesses, allowing attackers to skip identity checks entirely.
A critical flaw in the SaltStack documentation repository allowed attackers to steal secrets by injecting malicious code into forked pull requests before a recent patch.
A zero-day vulnerability is a software flaw unknown to the vendor, leaving users exposed until a patch exists, often exploited before detection.
Self-hosted GitLab instances require strict network segmentation and least-privilege database access to prevent lateral movement after an initial breach.
IBM Db2 Mirror for i versions 7.4 through 7.6 contain a critical flaw allowing authenticated attackers to escalate privileges and execute code.
A critical flaw in MarkLogic Server allows remote attackers to execute code with elevated permissions by bypassing required privilege checks.
A critical flaw in GitLab CI/CD allows unauthenticated attackers to run arbitrary code. Self-managed users must upgrade immediately to mitigate this severe risk.