Threat Intelligence
Alert Triage Mistakes and Fixes for Security Analysts
Triage failures often stem from cognitive biases and tool misconfiguration rather than a lack of technical skill or insufficient data volume.
Triage failures often stem from cognitive biases and tool misconfiguration rather than a lack of technical skill or insufficient data volume.
Hybrid cloud architecture increases the attack surface by combining public scalability with private control, creating complex identity and data flow challenges.
Administrators often enable PowerShell execution by default, creating a persistent backdoor that attackers exploit without installing any external malware or tools.
Display names and SPF records do not guarantee sender identity, leaving your inbox vulnerable to sophisticated impersonation attacks that bypass standard filters.
A single misconfigured SPF record can block legitimate invoices while still allowing attackers to send convincing messages from your domain.
Threat intelligence transforms raw data into context that predicts attacker behavior, allowing defenders to block threats before they reach critical systems.
Scammers rely on your willingness to bypass security controls, not your technical ignorance, to install malware and steal credentials from your device.
Social engineering bypasses technical defenses by manipulating human psychology, making it the human equivalent of a cyber attack rather than a separate category.
Attackers exploit organizational hierarchy and urgency rather than technical vulnerabilities to trick employees into moving money or data.
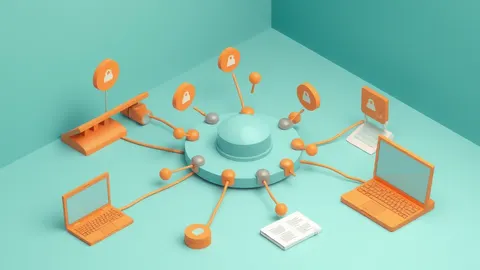
Security orchestration, automation, and response platforms reduce manual toil by connecting disjointed tools into a single workflow engine that executes predefined actions.
Prevention systems block traffic automatically while detection systems only alert, creating a distinct trade-off between security speed and the risk of blocking legitimate user activity.
Account takeover protection relies on detecting behavioral anomalies rather than just verifying static credentials, because stolen passwords often look identical to legitimate ones.
High alert volume trains analysts to ignore warnings, turning your security stack into a silent monitor that hides real attacks in plain sight.
Small teams can prioritize patching by focusing only on vulnerabilities that attackers are actively using in the wild right now.
Cross-site scripting fails when the browser treats user input as data rather than executable code, breaking the attack chain before any payload runs.
Authentication bypass flaws often stem from predictable logic errors in code rather than complex cryptographic weaknesses, allowing attackers to skip identity checks entirely.
Attackers exploit the trust you place in automated patching mechanisms to bypass perimeter defenses and install persistent backdoors on your network.
A zero-day vulnerability is a software flaw unknown to the vendor, leaving users exposed until a patch exists, often exploited before detection.
Gift card fraud often hides in standard procurement workflows, bypassing security filters by mimicking legitimate vendor transactions and internal requests.
Resilience fails when teams optimize for uptime alone, ignoring the silent decay of configuration drift and untested recovery paths that surface during actual failures.
Self-hosted GitLab instances require strict network segmentation and least-privilege database access to prevent lateral movement after an initial breach.
Attackers combine usernames from public sources with leaked passwords to bypass single-factor authentication, making username exposure as dangerous as password theft.
Network scanning reveals hidden infrastructure by exploiting protocol quirks, often bypassing perimeter defenses that only inspect established connections.
A zero-day exploit targets unknown flaws that vendors cannot patch, forcing defenders to rely on behavior detection rather than signature updates.